

AI & Emerging Tech
Uber rolls out ChatGPT Work to 30,000 employees: 11 companies that have restricted AI tools



As Uber expands access to OpenAI’s workplace AI agent, earlier restrictions at major companies reveal why data security remains central to enterprise AI adoption.
Uber is giving more than 30,000 employees access to ChatGPT Work, expanding from an initial pilot of 1,000 people. The company-wide rollout puts an AI agent designed for complex, multi-step tasks into the hands of teams across its global workforce.
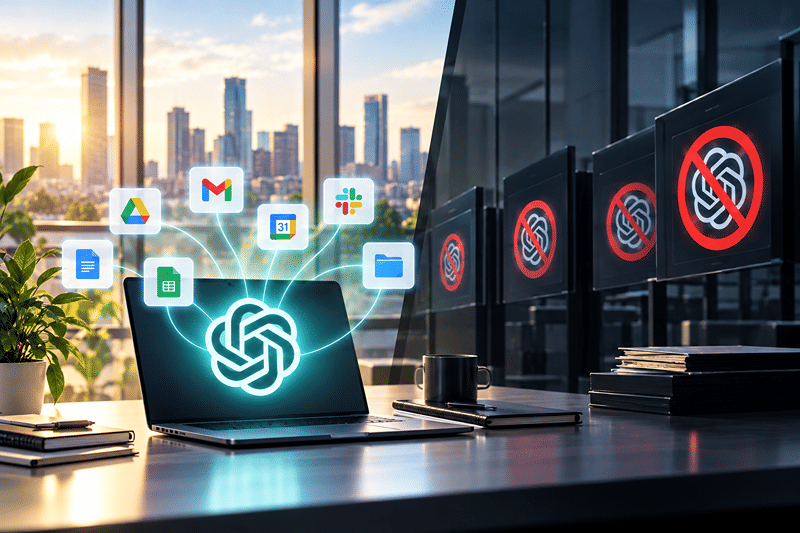
According to OpenAI’s announcement, ChatGPT Work can connect with workplace tools such as Google Drive, Gmail, Google Calendar and Slack. Employees can use it to research information, prepare meeting briefs, analyse data, create presentations and complete workflows across applications.
The move highlights a key shift in workplace AI: businesses are exploring how to give employees more powerful tools while keeping sensitive information protected. Several major companies have previously restricted ChatGPT or other public generative AI platforms, citing concerns about confidential data, source code and compliance.
Here are 11 companies that have restricted workplace AI use, based on reports from Fortune, Bloomberg, Axios, Forbes and HR Brew. The restrictions below reflect published reporting and should not be taken as confirmation of each company’s current policy.
1. Apple restricted ChatGPT to protect its proprietary information
For a company that guards its product plans and software closely, putting confidential information into a public AI tool presents a clear risk.
Apple restricted employee use of ChatGPT and other external AI tools, including GitHub Copilot, according to reports published in 2023. The concerns centred on the possibility of employees exposing proprietary source code or other confidential company information.
The restriction highlighted a challenge for technology companies: AI can help employees work faster, but the information entered into external tools also needs protection.
2. Samsung banned generative AI after employees uploaded sensitive data
Samsung Electronics introduced a ban on generative AI tools on company devices and internal networks after employees reportedly uploaded sensitive information to ChatGPT, Bloomberg reported.
The incidents included employees sharing proprietary source code and other internal material while seeking help with work tasks. The company’s response showed how quickly an attempt to use AI for productivity can become a data-security concern.
Samsung’s case became a prominent example of the risks companies face when employees use public AI tools without adequate safeguards.
3. JPMorgan Chase restricted ChatGPT amid compliance concerns
In banking, the question is not simply whether an AI tool can complete a task, but whether employees can use it within the organisation’s compliance requirements.
JPMorgan Chase restricted employee access to ChatGPT, according to reporting by Axios and other outlets in 2023. The move was linked to controls around third-party software and concerns about data privacy and compliance.
The restriction reflected the challenges financial institutions face when assessing public AI tools for work involving confidential business or client information.
4. Bank of America placed ChatGPT on its unauthorised-app list
Bank of America included ChatGPT among applications employees were not authorised to use for business, Fortune reported in 2023.
The approach put the chatbot within the bank’s broader controls over third-party software. For financial institutions, managing which applications employees can use is one way to limit the risk of sensitive information reaching external services.
5. Citigroup limited employee access to ChatGPT
Citigroup also restricted ChatGPT through its controls on third-party software, Fortune reported.
The bank was examining the technology’s potential benefits and risks, according to the report. Its position illustrated how financial services companies could explore generative AI while limiting employee use of public tools.
6. Goldman Sachs restricted public AI while exploring internal uses
Goldman Sachs restricted employee access to ChatGPT through its third-party software controls, Forbes reported in 2023.
The investment bank was also exploring internal generative AI applications for tasks such as summarising information and supporting research workflows. The contrast points to a distinction between blocking uncontrolled access and investigating AI within a more managed environment.
7. Deutsche Bank disabled employee access to ChatGPT
Deutsche Bank disabled employee access to ChatGPT, according to reports by Fortune and Forbes.
The restriction was associated with concerns about confidential banking information and potential data leakage. The bank was also assessing how AI could be used within controlled environments.
8. Northrop Grumman restricted public AI tools
For a defence company, the consequences of exposing sensitive information can extend well beyond commercial confidentiality.
Northrop Grumman restricted access to public AI tools, HR Brew reported. The company’s approach reflected the need to vet external services before employees use them for work involving sensitive corporate or defence-related information.
9. Verizon blocked ChatGPT on corporate systems
Verizon made ChatGPT inaccessible through corporate systems, Fortune reported in 2023.
The telecommunications company cited concerns about losing control over sensitive information, including customer data and source code. The restriction focused on preventing uncontrolled use through workplace systems.
10. Accenture limited generative AI use in client-related work
Consulting firms often handle confidential information belonging to multiple clients, making the use of public AI tools a question of both data protection and professional responsibility.
Accenture introduced restrictions on employee use of generative AI for coding and client-related work, according to HR Brew. The reported guidance limited use without appropriate permission and cautioned employees against sharing confidential company or client information.
The distinction matters: restrictions on particular tasks or data do not necessarily amount to a company-wide ban on every AI application.
11. Amazon warned employees not to share confidential information with ChatGPT
Amazon warned employees against entering confidential company information into ChatGPT, Fortune reported, citing Business Insider.
The company also directed engineers towards its AI coding assistant, CodeWhisperer, in certain contexts. The reported approach focused on protecting sensitive information rather than imposing a blanket ban on every generative AI tool.
Uber’s approach highlights the enterprise AI shift
Uber’s rollout brings the debate into focus. Rather than relying only on restrictions, the company is expanding access to an enterprise AI agent supported by approved integrations, employee training and an internal AI skills library.
The comparison does not establish that Uber’s approach is inherently safer, or that the other companies still enforce their earlier policies. It shows how organisations have taken different approaches to balancing AI access with the protection of sensitive information.
For Indian businesses considering enterprise AI, the central questions are practical: what information can employees share, which systems can an agent access, and how will its actions be supervised?
As AI tools move from generating answers to completing multi-step work, companies will need policies that address not only who can use AI, but also what it can access and do.
Topics
Author
Loading...